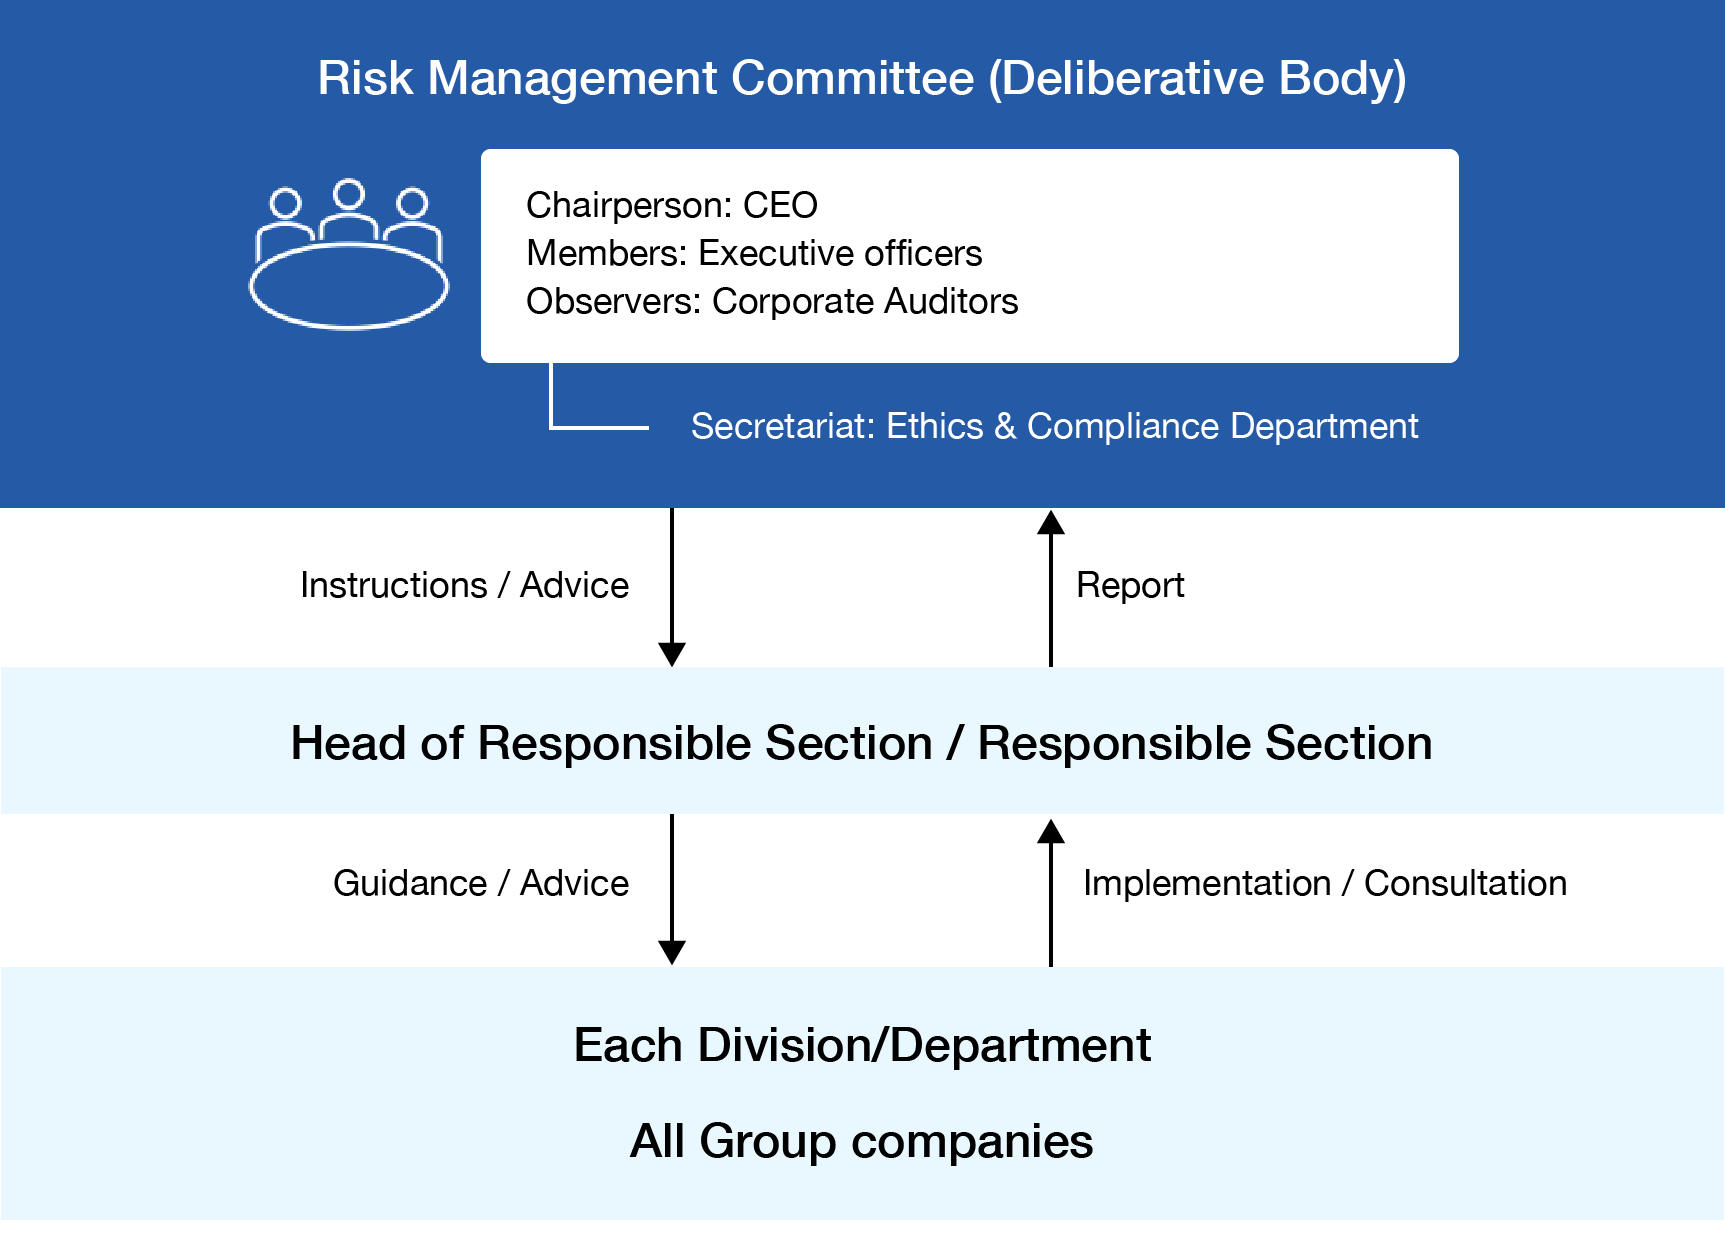
The Group has defined “Risk Management Rules” and is taking appropriate measures to consider risks from the perspectives of both opportunities and threats in order to maintain and enhance corporate value. In the event that a risk materializes, we are working to construct systems to minimize loss. The Risk Management Committee, which has been established to oversee these systems, determines risk management policies, and in line with these policies, manages risks that impact on the entire Group and require priority response. Additionally, the status of risk management activities is reported regularly to the Board of Directors.
Risk management system
The Group has formulated a business continuity plan (BCP) to prepare for threats to business continuity such as natural disasters and outbreaks of infectious disease, war, and acts of terrorism, and reviews it regularly. We have prepared measures to allow us to offer patients a stable supply of pharmaceuticals in the event of a crisis.
Additionally, we conduct training for executive officers and personnel responsible for operations that must continue even during disasters, and operate a platform for the collection and sharing of information on damage inflicted. These efforts are intended to ensure that there are systems in place to support prompt decision-making and strengthen our crisis response capabilities.
With regard to supply chain business continuity, we have established and operate systems that allow us to rapidly ascertain the impact of disasters on our contractors in Japan and overseas and share this information among relevant parties to ensure that we can offer a stable supply of pharmaceuticals. Through initiatives such as these, we work to identify risks across the entire supply chain, respond promptly, and effect an early recovery. Going forward, we will cooperate with contractors to strengthen our risk management systems and improve their effectiveness.
The Company has established the TP-CSIRT (Tanabe Pharma-Computer Security Incident Response Team) Secretariat, which handles information management and incident response.
Main roles of the TP-CSIRT Secretariat
- Implementation of information management measures and issuance of instructions, requests, or recommendations to internal departments
- Provision of education and training related to information management
- Responding to consultations from employees regarding information management
- Instructions, advice, requests, internal coordination, and reporting on responses to accidents or violations related to information management
Furthermore, to respond to the growing threats associated with the increasing complexity of our IT infrastructure, the Group implements measures to ensure the safe and stable use of information and data communications technologies, such as enhancing network security and security checks when using cloud services. We are also taking steps to improve security, including that of our supply chain, by checking our business partners’ security.
In preparation for damage mitigation and early recovery in the event of an incident, we are examining our response system and flow in conformity with the above incident prevention measures.
The leakage of personal information not only harms third parties but could also seriously damage the credibility of the Company and cause irreparable loss.
The Group complies with Japan’s Act on the Protection of Personal Information, as well as with international laws and regulations such as the European Union’s General Data Protection Regulation. Furthermore, taking the Group’s business activities in Japan and overseas into account, we will reassess our internal rules and ensure rigorous management of information.
To cater to a diverse range of work styles, we have installed a SASE (Secure Access Service Edge) platform to provide a safe environment that is comfortable to use, regardless of location. SASE allows secure use of a network while applying appropriate access control based on user and device conditions.